
Sustainable Risk Control
Risks and opportunities are often two sides of the same coin. When one comes, the other follows. The same applies to corporate development. The world was not devoid of challenges in 2025. The U.S. rattled the world with reciprocal tariffs; exchange rates grew increasingly volatile; the Russo-Ukrainian War and conflicts in the Middle East were yet to subside; domestic demand weakened in mainland China. At a time like this, the presence of a robust risk control mechanism is of vital importance, and only through such a mechanism can operational risks be minimized, growth opportunities fostered and corporate sustainability fulfilled.
To reinforce corporate governance and establish sound risk control to reach corporate targets, the Board approved Risk Control Policy on November 12, 2020. The objective is to ensure sustainable management, reduce damages and enhance corporate profit. Risks and opportunities should be evaluated accordingly for all business conducts to identify, evaluate, monitor and control risks, keeping risks within manageable range to rationalize risks and benefits.
FENC established a three-tiered organizational structure for risk control. From the first to third are all Businesses, administrative departments and applicable units; the Risk Management Team; internal audit, and their duties and responsibilities are stated in the Risk Management Policies. An emergency response team is to be established to form immediate responses to sudden material risk events, ensure regulatory compliance and minimize potential losses and impacts. Monthly briefings covering issues such as management, sales, industrial operations, energy conservation and carbon reduction are held to keep the Board and senior executives informed and maintain sound decision-making, and risk control indicators have been incorporated as part of the performance review.
FENC has adopted the International Financial Reporting Standards (IFRS) Sustainability Disclosure Standards S1 General Requirements for Disclosure of Sustainability-related Financial Information and S2 Climate-related Disclosures to identify sustainability- and climate-related risks and opportunities that can reasonably be expected to affect the Company's outlook. The procedures follow the framework of FENC’s Risk Management Policies.
⇥ Risk Management Policies
Structure of Risk Control Organization
The Board acts as the highest decision-making entity for risk control, which oversees the operation of risk control policies and management mechanisms to ensure the effectiveness. All business units, administrative departments and applicable units shall establish risk appetite and determine whether the risks exposed for achieving goals are acceptable given the established risk appetite. The Risk Management Team shall establish qualitative and quantitative criteria for management, review risk control issues and present risk control reports to the Board at least once a year.
First line of defense | All Businesses, administrative departments and applicable units | All Businesses, administrative departments and applicable units shall clearly identify major risks associated with their operations, conduct risk management and implement appropriate risk assessments in response to factors such as changes in the internal, external and regulatory environments. Regular reports on the risk management status shall be presented to the Risk Management Team under Corporate Management. |
Second line of defense | Risk Management Team | The Risk Management Team under Corporate Management oversees the entire risk management practices at FENC. The team is responsible for developing risk management policies, frameworks and mechanisms as well as qualitative and quantitative management standards. The team also conducts monthly reviews over risk control measures reported by various units in line with their assigned responsibilities. Additional tasks include examining issues related to risk management, monitoring the implementation and coordination of overall risk management initiatives, and presenting the risk management report to the Board at least once a year. |
Third line of defense | Internal audit | FENC’s internal audit units conduct operational risk assessments and audits through the internal control system and provide improvement recommendations in the audit report. In addition to the three lines of defense, an emergency response team shall be established in the event of a sudden material risk event with the potential of major impacts on the Company. The response team shall address risk situations immediately and communicate with internal and external stakeholders to ensure regulatory compliance and minimize potential losses and impacts. |
Identification and Management of Major Risks
Material Risks
FENC identifies potential risks through a systematic risk assessment mechanism. Potential risks and sources relevant to operation are identified by each department, followed by prioritization and evaluation by the senior management. The likelihood of each risk event and its magnitude of impact on FENC’s operation are assessed during the process. Based on this assessment framework, the followings are identified as areas with significant risk exposure during the reporting year:
(1) Financial Risk (Exchange Rate Fluctuation): Potential financial impact resulting from exchange losses due to international political and economic conditions.
(2) Information Security Risk: Potential impact resulting from business interruption and pecuniary penalties caused by ransomware attacks. For details on measures established and mitigation actions, please refer to the corresponding chapters in the FENC Sustainability Report or FENC Annual Report.
Major Risk and Response
Risk Type | Description | Potential Impact If Unaddressed | Strategy |
Financial Risk | Risks affecting financial targets caused by fluctuations in domestic and foreign interest rates, exchange rates and customer credit |
|
|
Strategic and Operational Risk | Risks caused by business strategies, domestic and international market competition, industry cooperation and changes in policies and regulations. |
|
|
Information Security Risk | Network technology is progressing at an expeditious rate. With the prevalence of remote work and cloud computing, the corporate world is facing cybersecurity threats that are growing in diversity and complexity. Common threats such as ransomware, phishing and social engineering attacks are also striking wider targets with more sophistication , adding hurdles when it comes to defending corporate operations and data security. |
| FENC has implemented the following five mitigating actions:
|
| Environmental, Carbon Reduction and Energy Risk | Risks caused by climate change, geographical resources, global carbon-reduction progress, energy and applicable fiscal and tax policies | Fines, lawsuits, protests, boycotts, market pressure or competitive disadvantages due to inadequate management of GHG as well as energy and resource consumption, damage to ecosystems and violations of environmental regulations |
|
ESG Risks | Risks caused by the inability to meet stakeholder expectations in ESG performance |
|
|
The financial incentive system for Directors and management also incorporates annual major risk indicators, such as Financial Risk; Strategic and Operational Risk; Information Security Risk; Environmental, Carbon Reduction and Energy Risk; and ESG Risks.
⇥Linkage Between Annual Performance Appraisal Framework and Executive Compensation
Emerging Material Risk
Emerging Risk | Description | Impact | Mitigating Actions |
Global Trade Realignment Risk | In 2025, the global political-economic landscape remained volatile. The United States' reciprocal tariff policies intensified global trade tensions, increasing pressure on supply chains and international security frameworks. The Russia–Ukraine war continued, conflicts in the Middle East remained frequent, and strategic competition between the United States and China further extended into technology, energy, and industrial policy. As a result, global supply chain configurations and the cross-border investment environment faced increasing uncertainty, further elevating geopolitical risks. These political conflicts have not only disrupted the free flow of goods and technologies, but also undermined the established order of globalization and international trade. The evolving geopolitical risks have eroded market efficiency, exerting profound impacts on Taiwan’s economy and security. They continue to disrupt business models and increase costs for enterprises. |
|
|
| Generative AI and Agentic AI Governance Risk | With the rapid development of Generative AI, Agentic AI, and autonomous decision-making technologies, AI is evolving from a content-generation tool into a new type of technology capable of independently planning and executing tasks, integrating with enterprise systems, and supporting decision-making. As related technologies, governance frameworks, and regulations continue to evolve, organizations may face emerging risks such as model errors and hallucinations, prompt injection, uncontrolled autonomous agent behavior, inadequate access control, improper use of sensitive data, reliance on third-party AI services, and regulatory compliance challenges. As AI becomes increasingly embedded in core enterprise systems, business processes, and decision-making mechanisms, these risks may extend beyond traditional information security, data governance, and operational management, creating new long-term challenges for corporate governance and risk management. | The Company continues to promote Generative AI, AI Agents, and other intelligent applications. AI is expected to be increasingly used in information analysis, process automation, operational management, and decision support. Without appropriate AI governance and risk management mechanisms, model errors, improper autonomous agent actions, insufficient access controls, or inappropriate input of sensitive data could result in incorrect decisions, information leakage, system disruptions, or impacts on business operations. In addition, as AI-related regulations and governance requirements continue to develop globally, failure to keep pace with these changes and update internal management mechanisms in a timely manner may lead to regulatory compliance, data governance, corporate reputation, and third-party AI service management risks, increasing uncertainty in the Company’s operations and governance. | Establish and continuously update AI management policies and Agentic AI usage guidelines.
|
Principles, Mitigation and Control Measures, and Identification and Management Procedures
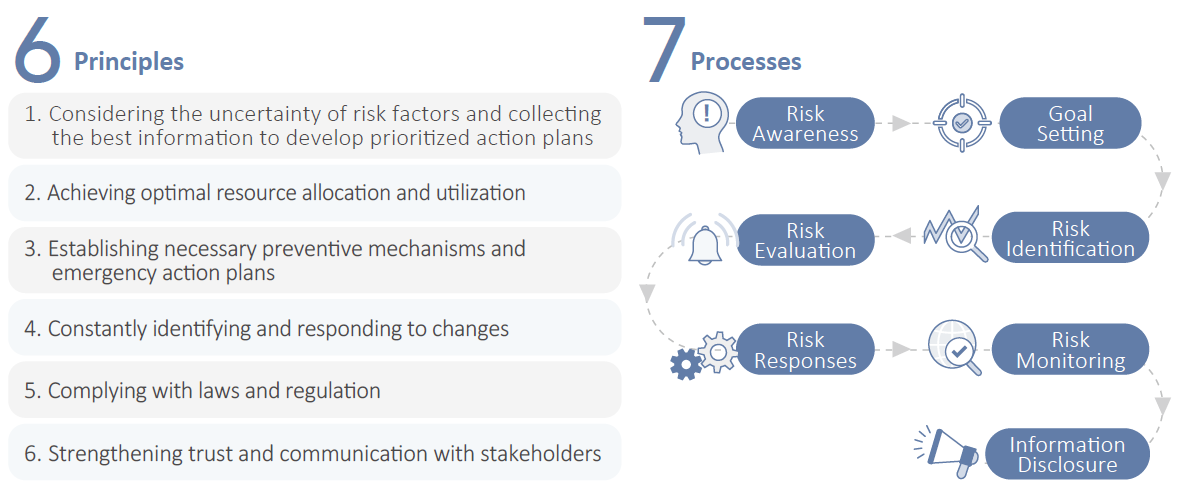
FENC establishes risk indicators and stays on top of environmental and regulatory changes through regular tracking. Once the risks are defined through internal meetings, evaluation is conducted by designated units on the potential threats and impacts on the Company to formulate action plans. Responses and control measures are carried out through special projects. The implementation and progress are reported to the highest governing entity on a regular basis.
Risk Control Mechanism
The Company’s risk management mechanism consists of risk alert system, regulatory compliance system,and etc. The Company offers the staff regular training to be risk awareness. Furthermore, risk control is implemented in conjunction with the internal audit system and is conducted through various monthly meetings, covering risk issues such as management and sales, industry management, environment sustainability and GHG reduction, etc.
1. Risk Alert System: Conduct regular follow-ups and examine corporate risks to establish advanced corresponding measures.
2. Regulatory Compliance System: Regularly implement self-evaluation on compliance to reduce risk of violation
3. Risk Ranking Project: Regularly conduct plant risk ranking projects to reduce operational risks.
4. Risk Control Training: Implement staff training to increase risk awareness.
5. Internal Control System: Oversee and manage risks through internal control system.
6. Regular Meeting: Conduct multiple monthly meetings to ensure management of and focus on risk issues from the highest governing entity.
FENC Regular Meetings
The risk management and implementation of 2025 have been reported in the Audit Committee on November 5, 2025 and the Board meeting on November 7, 2025.
■ Environment ● Social ◆ Governance
Important Meeting | Interval | Corresponding Issue | Highest Ranking Attendee | |
Board Meeting | Board Meeting | Quarterly | ■ ● ◆ | Chairman |
Audit Committee | Quarterly | ◆ | Independent Directors and Directors | |
Remuneration Committee | Semi-Annual | ◆ | ||
Sustainability Committee | Semi-Annual | ■ ● ◆ | ||
Themed Meeting | Management Meeting | Annual | ■ ● ◆ | Chairman/Vice Chairman |
Human resources management and development | Semi-Annual | ● ◆ | ||
Special report on R&D | Annual | ■ ◆ | ||
Seminar on industry strategies | Semi-Annual | ◆ | ||
Budget review | Annual | ◆ | ||
Environment sustainability | Annual | ■ | ||
Regular Meeting | Operation review meeting | Monthly | ■ ● ◆ | |
Sales Meeting | Semi-Monthly | ◆ | Presidents of Petrochemical Business, Polyester Business and Textile Business | |
Risk management meeting | Monthly | ■ ● ◆ | President of Corporate Management | |